Ready reckoner
Programme building blocks
Governance foundation (mandate, roles, policies) → pillars: inventory · risk assessment · notices, consent and rights · third parties and transfers · security and breach response · training and audit.
| Line | Who | Job |
|---|---|---|
| First | Business and system owners | Manage privacy risk day to day |
| Second | Privacy function / DPO | Set standards, advise, oversee |
| Third | Internal audit | Independent assurance |
Policy hierarchy: policy → standards → procedures → guidelines. Internal policy ≠ external notice.
Cycle: Plan (laws, gaps, roadmap) → Do (controls, training) → Check (metrics, audits) → Act (fix, update).
Maturity: initial → repeatable → defined → managed → optimised.
Know your data
| Artefact | Answers |
|---|---|
| Data inventory | Where is personal data? |
| Record of processing | Why and how is it processed? |
| Data-flow map | How does it move, to whom, which countries? |
RoPA fields: activity + owner · purpose · legal basis · data subjects · data categories · recipients · transfers · retention · security · systems · DPIA status. Build with workshops + automated discovery + process hooks.
DPIA
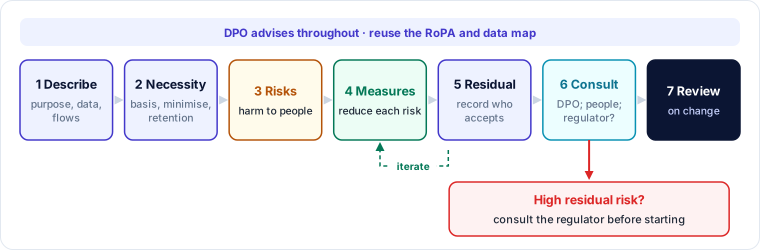
Triggers (two or more → DPIA): profiling · sensitive data at scale · children / vulnerable · systematic monitoring · new technology · matching datasets · blocking a service or right · tracking.
Steps: describe → necessity → risks to people → measures → residual risk → consult (DPO; regulator if high risk remains) → sign off and review.
Privacy by design: proactive · private by default · embedded · positive-sum · lifecycle security · transparency · user-centric. Patterns: minimise, hide, separate, aggregate, inform, control, enforce, demonstrate. Privacy threats: LINDDUN.
Vendors and transfers
Vendor lifecycle: plan → due diligence → contract (DPA) → monitor → exit, scaled by risk tier.
DPA must cover: instructions · confidentiality · security · sub-processors · assistance · breach notice · deletion/return · audits · transfers.
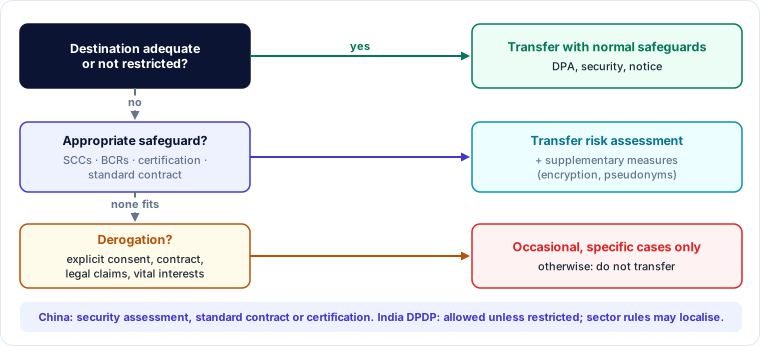
| Transfer tool | Note |
|---|---|
| Adequacy | Country-level approval (EU–US DPF for certified firms) |
| SCCs / standard contract | Plus transfer risk assessment |
| BCRs | Intra-group, approved |
| Certifications | CBPR, PIPL certification |
| Derogations | Occasional, specific cases only |
| DPDP | Allowed except restricted countries; sector rules (e.g. RBI) may require localisation |
Supplementary measures: exporter-held encryption keys, pseudonymisation, split processing, transparency commitments.
Visual summary