Ready reckoner
Three ideas
| Term | Protects | Key question |
|---|---|---|
| Privacy | A person's right to control information about them | Should this happen at all? |
| Data protection | The use of personal data | Is this use lawful, fair and limited? |
| Information security | All information (CIA) | Is it protected from loss and misuse? |
Personal data tests
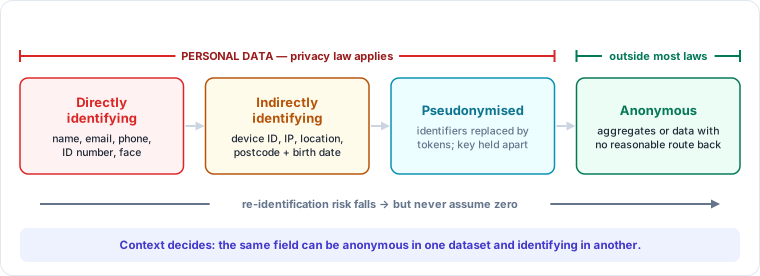
- Relates to a living person, and the person is identified or identifiable by means reasonably likely to be used.
- Indirect identifiers: device and cookie IDs, IP addresses, location, employee numbers.
- Quasi-identifiers (postcode + birth date + gender) combine to single people out.
- Pseudonymised = still personal (key exists). Anonymised = outside most laws, but only if re-identification is not reasonably likely. Test it.
- Sensitive: health, genetic, biometric, ethnicity, religion, politics, union, sex life, plus financial, ID numbers and precise location in some laws; children's data has its own rules.
Roles across laws
| Role | GDPR | DPDP | CCPA | PIPL |
|---|---|---|---|---|
| Individual | Data subject | Data Principal | Consumer | Individual |
| Decides why and how | Controller | Data Fiduciary | Business | PI handler |
| Acts on instructions | Processor | Data Processor | Service provider | Entrusted party |
- Whose purpose? That party is the controller. A processor that uses data for its own ends becomes a controller.
- Joint controllers decide together and must allocate duties; independent controllers each pursue their own purposes.
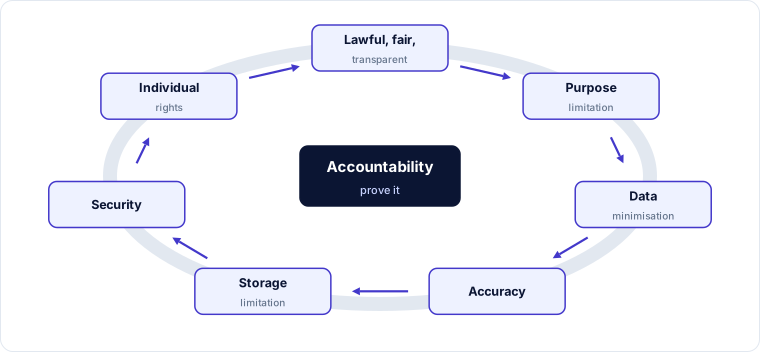
Core principles (and one control each)
| Principle | Control |
|---|---|
| Lawful, fair, transparent | Legal-basis record, clear notice |
| Purpose limitation | Purpose register, compatibility check |
| Minimisation | Field-by-field justification |
| Accuracy | Validation, self-service correction |
| Storage limitation | Retention schedule, auto-delete |
| Security | Access control, encryption, logging |
| Individual rights | Data map, request workflow |
| Accountability | Records, assessments, contracts, training, audits |
Law landscape
- Models: comprehensive (GDPR, DPDP, LGPD, PIPL), sectoral (US HIPAA, GLBA, COPPA), hybrid (about 20 US states plus federal sector laws).
- Scope triggers: establishment, targeting (offering goods or services, monitoring behaviour), or thresholds (US states).
- Multi-law compliance: common baseline + local overlays; apply the strictest rule globally where cheaper.
- Headline penalties: GDPR up to €20m or 4% of turnover; DPDP up to ₹250 crore per breach type.
Visual summary