Ready reckoner
Appropriate security
- Risk-based: sensitivity, volume, vulnerability, state of the art, cost. Test controls regularly.
- DPDP Rules minimums: encryption, obfuscation or masking, access control, logging and monitoring, backups, processor contracts. Failing reasonable safeguards: up to ₹250 crore.
| Lifecycle | Key controls |
|---|---|
| Collect | Minimise, classify |
| Store | Encrypt, least privilege |
| Use | Pseudonymise, mask, log access |
| Share | DPA, DLP, transfer safeguards |
| Retain | Schedule, legal hold |
| Delete | Reach every copy: replicas, exports, processors, backups |
Retention schedule: record type → drivers (law, claims, need) → period + trigger → end action → automate.
PETs (mature → emerging): masking · aggregation / k-anonymity · pseudonymisation · differential privacy · synthetic data · federated learning · trusted execution · secure MPC · homomorphic encryption.
Breaches
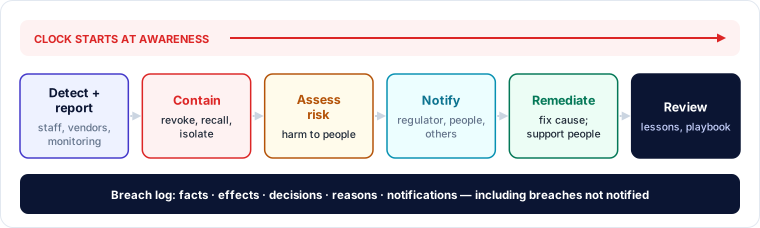
Types: confidentiality · integrity · availability. Lifecycle: detect → contain → assess → notify → remediate → review; log every breach.
Risk factors: data type · volume · identifiability (encryption) · consequences · vulnerability · recipient · containment.
| Rule | Deadline |
|---|---|
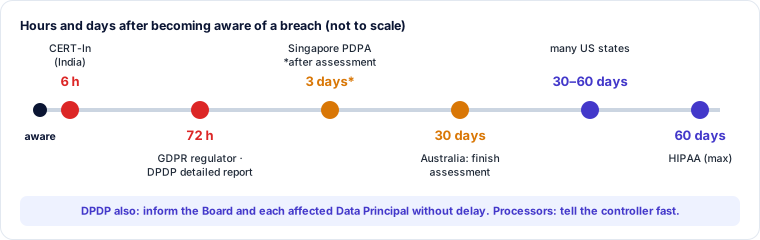
| CERT-In (India) | 6 hours |
| GDPR regulator | 72 hours (individuals if high risk, without undue delay) |
| DPDP | Board + each Data Principal without delay; detailed report to Board in 72 hours |
| Singapore PDPA | 3 days after assessing notifiable |
| Australia NDB | Assess within 30 days |
| HIPAA | No later than 60 days |
Everyday technology
- EU/UK: prior consent for non-essential cookies; strictly necessary exempt. US states: opt-out of sale/sharing, honour GPC. DPDP: tracking needs consent; none directed at children.
- Tracker governance: scan · classify · block by default · tag approval · no trackers on sensitive pages.
- AI: approved tools, no-training contracts, DLP; training data needs basis, notice, minimisation, rights plan, DPIA.
- Monitoring: necessary, proportionate, transparent, assessed. CCTV: signs, short retention. Biometrics: offer alternatives, store templates, delete at exit.
Assurance and improvement
KPIs (performance) + KRIs (early warning). Assurance: self-assessment → privacy monitoring → internal audit → external audit / certification (ISO/IEC 27701, CBPR). Check certificate scope.
Training: role-based, regular, practical, measured; blame-free reporting. Complaints: acknowledge, investigate, respond, fix root cause. Regulators: route, preserve, respond, remediate, record.
Visual summary